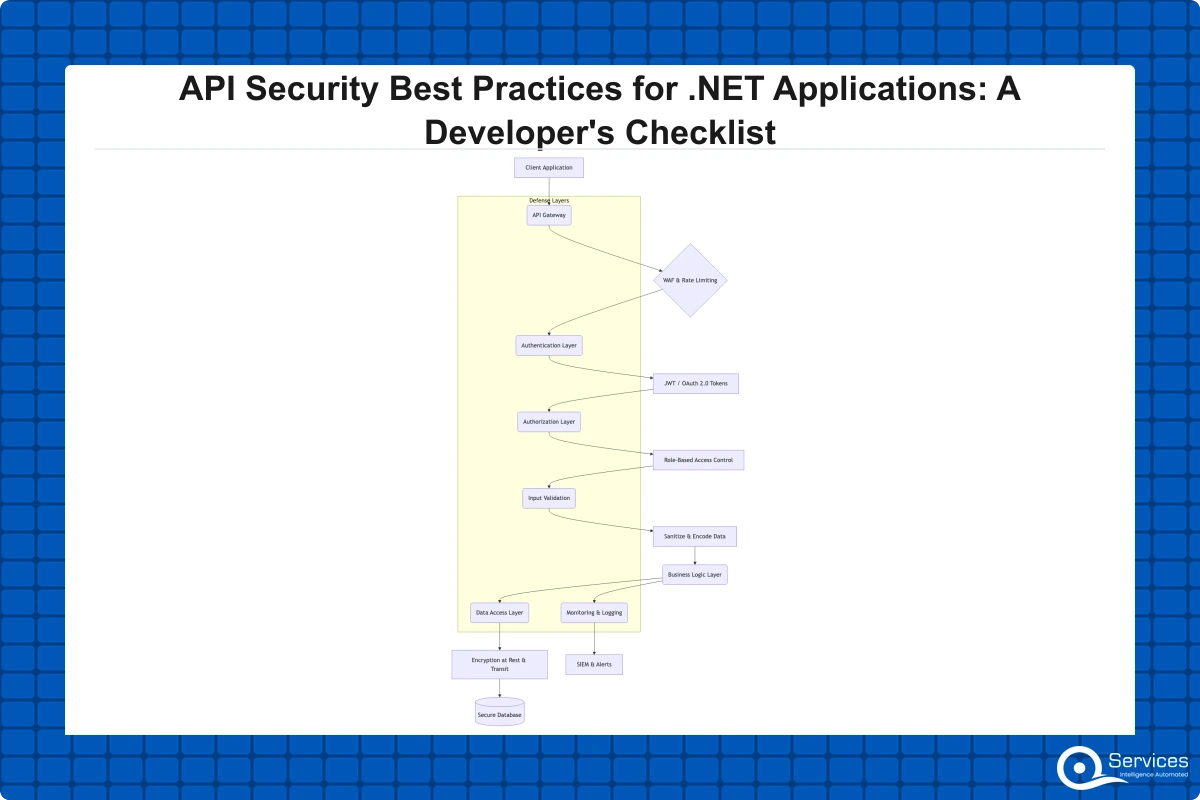
A single unsecured endpoint can leak millions of records before anyone notices. For .NET teams shipping APIs into production, api development services that ignore security at the design stage create the most expensive kind of technical debt: the kind that shows up in a breach disclosure. This checklist walks through the controls that matter for .NET 8 and .NET 9 APIs, from authentication and input validation to rate limiting, logging, and dependency hygiene. Whether you run ASP.NET Core Web APIs behind Azure API Management or expose minimal APIs from containerized microservices, the rules below are the ones our team enforces on every engagement.
In This Article, You'll Learn
Why API Security Deserves Its Own Checklist in .NET
Authentication: Lock the Front Door First
Authorization: Authentication Is Not Enough
Input Validation and Model Binding Safety
Rate Limiting and Resource Protection
Eager to discuss about your project?
Share your project idea with us. Together, we’ll transform your vision into an exceptional digital product!
Why API Security Deserves Its Own Checklist in .NET
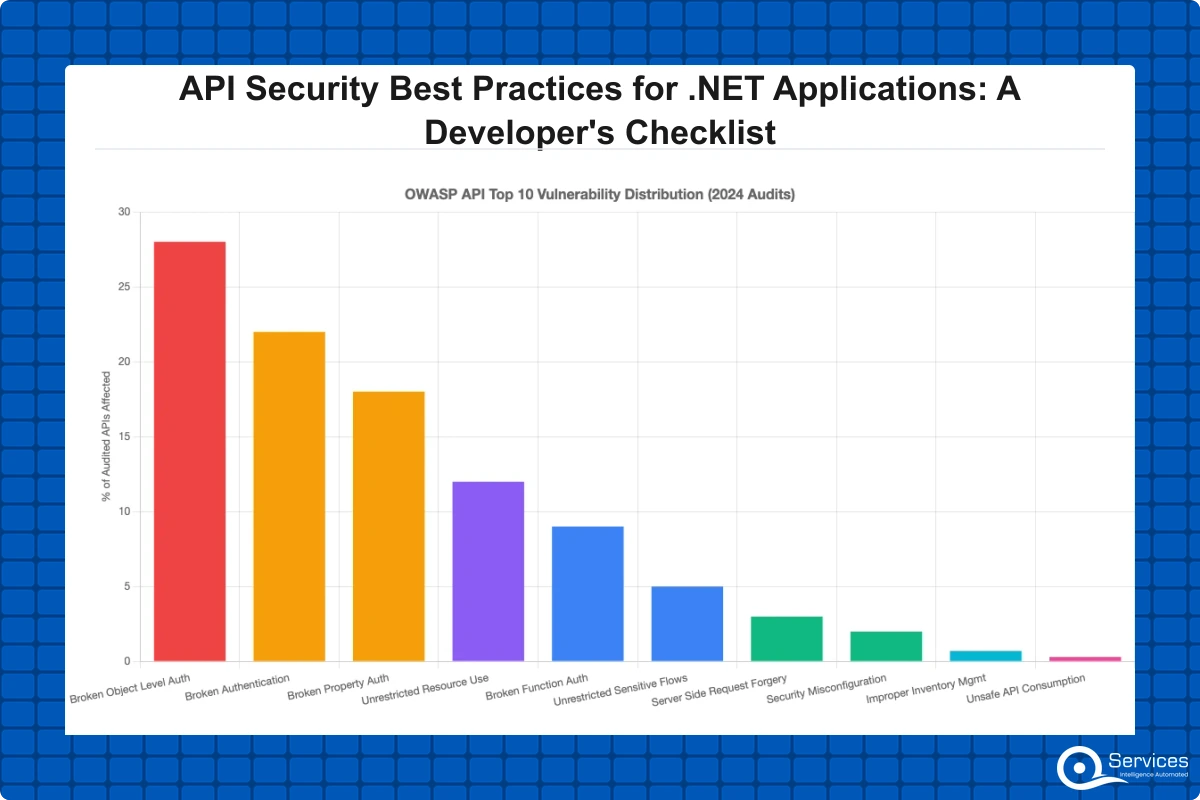
The attack surface of a modern .NET API is wider than most teams admit. You have JWT validation, model binding, serialization, EF Core query construction, third-party NuGet packages, and the infrastructure layer surrounding it all. OWASP's API Security Top 10 lists broken object-level authorization, broken authentication, and unrestricted resource consumption as the top three risks. Each one has a specific .NET fix, and skipping any of them is the difference between a passing pen test and a Monday morning incident call.
The cost of getting it wrong
IBM's 2024 Cost of a Data Breach report puts the average breach at $4.88 million, with API-related incidents trending higher because of the volume of records exposed per event. For regulated sectors, healthcare, banking, logistics, that number climbs further once HIPAA, PCI-DSS, or SOX penalties enter the picture. The teams we work with through our azure consulting services typically discover three to five critical API issues during their first security review.
Key Insight IBM's 2024 Cost of a Data Breach report puts the average breach at $4.88 million, with API-related incidents trending higher because of the volume of records exposed per event.
What this checklist covers
This is not a theoretical guide. Every item below maps to a concrete .NET 8 or .NET 9 implementation detail, a NuGet package, a middleware configuration, or an Azure service. If you are evaluating a microsoft azure consulting company or running an internal review, use this as the baseline.
Authentication: Lock the Front Door First
Most API breaches start with weak or missing authentication. ASP.NET Core gives you the primitives, but defaults are not enough.
Use JWT with proper validation
When you call AddJwtBearer in Program.cs, validate every claim that matters: issuer, audience, lifetime, and signing key. Setting ValidateIssuerSigningKey = true is non-negotiable. Use TokenValidationParameters to pin the expected issuer to your Azure AD tenant or IdentityServer instance, never accept tokens from any issuer.
Prefer OAuth 2.0 and OpenID Connect over custom auth
Rolling your own token system is one of the fastest ways to introduce vulnerabilities. Microsoft Entra ID (formerly Azure AD) handles token issuance, rotation, and revocation properly. Our azure migration partner engagements almost always include moving customers off bespoke auth onto Entra ID with the Microsoft.Identity.Web package.
Enforce MFA on administrative endpoints
Any endpoint that can modify roles, create tenants, or export bulk data should require a recent MFA claim. ASP.NET Core supports this through AuthorizationPolicyBuilder.RequireClaim("amr", "mfa"). Pair it with conditional access in Entra ID for defense in depth.
Authorization: Authentication Is Not Enough
Knowing who the caller is does not tell you what they can do. Broken object-level authorization (BOLA) is the number-one API risk for a reason.
Implement resource-based authorization
Do not check roles at the controller level and call it done. Every endpoint that returns or modifies a specific resource needs an explicit check that the caller owns or has rights to that resource. ASP.NET Core's IAuthorizationService with custom AuthorizationHandler<TRequirement, TResource> classes is built exactly for this.
Use policy-based authorization, not just roles
Roles are coarse. Policies let you compose claims, scopes, and resource ownership into reusable rules. Define them once in Program.cs and apply them with [Authorize(Policy = "CanEditInvoice")]. This pattern scales when you move from a monolith to microservices, which is something our azure devops consulting services teams handle frequently.
Audit every authorization decision
Log the user ID, the resource ID, the policy evaluated, and the result. When a regulator asks who accessed patient record 12345 last March, you need an answer in minutes, not weeks.
Input Validation and Model Binding Safety
Trust nothing that comes in over the wire. Even authenticated clients can send malformed or malicious payloads.
Validate at the model level with FluentValidation or DataAnnotations
Use [Required], [StringLength], [Range], and [RegularExpression] on every DTO. For complex rules, FluentValidation gives you composable validators with better error messages. Return 400 Bad Request with a clear problem details response so clients know what to fix.
Guard against over-posting
Never bind directly to your EF Core entities. Always use DTOs that expose only the fields a client is allowed to set. Otherwise an attacker can include IsAdmin = true in a JSON body and your model binder will happily set it.
Sanitize anything that flows into queries or HTML
Parameterized queries through EF Core or Dapper prevent SQL injection by default, but raw SQL via FromSqlRaw reopens the door. If you must use it, use FromSqlInterpolated so parameters are escaped. For any string that might render in a browser, encode it with HtmlEncoder.Default.Encode.
Rate Limiting and Resource Protection
Unrestricted resource consumption is API Security Top 10 #4. .NET 8 finally shipped first-class rate limiting middleware, so there is no excuse to skip it.
Configure the built-in rate limiter
AddRateLimiter in Program.cs supports fixed window, sliding window, token bucket, and concurrency limiters. For most public APIs, a sliding window per authenticated user plus a stricter fixed window per IP for unauthenticated routes is a sensible default.
Set request size and timeout limits
Kestrel's Limits.MaxRequestBodySize defaults to 30 MB. For most JSON APIs that is far too generous. Drop it to what your largest legitimate payload actually needs. Combine with RequestTimeouts middleware in .NET 8+ to kill long-running requests that could exhaust thread pool resources.
Protect expensive endpoints separately
Report generation, bulk exports, and search endpoints deserve their own rate limit policies and often their own queue. Offload them to background workers via Azure Service Bus or Hangfire so a flood of report requests cannot take down your transactional endpoints.
Transport and Data Protection
Everything above assumes the bytes on the wire are confidential and untampered. That assumption needs enforcement.
Enforce HTTPS and HSTS
app.UseHttpsRedirection() and app.UseHsts() are one-liners. There is no reason not to use them in production. Set HSTS max-age to at least one year and include subdomains once you have validated all of them serve TLS.
Pin to TLS 1.2 or higher
In Program.cs, configure Kestrel to reject older TLS versions. Azure App Service and Azure Front Door let you enforce this at the platform layer, which is one less thing to misconfigure in code.
Encrypt sensitive data at rest
Use Azure Key Vault for connection strings, signing keys, and API secrets. The Microsoft.Extensions.Configuration.AzureKeyVault package makes this nearly invisible to application code. For column-level encryption in SQL Server, Always Encrypted with secure enclaves handles PII without exposing keys to the database server.
Dependency and Supply Chain Hygiene
Your API is only as secure as the weakest NuGet package you ship.
Run dotnet list package --vulnerable in CI
Make this a required check in your azure devops consulting services pipeline or GitHub Actions workflow. Fail the build on any high or critical vulnerability. Pair it with Dependabot or Renovate to get automated PRs for updates.
Pin package versions and use lock files
Floating versions like [8.0.*] mean a transitive dependency update can change your binary surface overnight. Use --use-lock-file with dotnet restore and commit the lock file.
Verify package signatures
NuGet supports signed packages. Configure your nuget.config to require signed packages from trusted authors for production builds. This is one of the controls a serious azure managed services provider should be running by default.
Logging, Monitoring, and Incident Response
You cannot defend what you cannot see. Insufficient logging shows up in nearly every breach post-mortem.
Log security-relevant events with structured logging
Use Serilog or the built-in ILogger with structured properties. Log authentication failures, authorization denials, rate limit hits, and any exception that surfaces from your data layer. Ship logs to Azure Monitor or Log Analytics for centralized querying.
Never log secrets, tokens, or PII
This is the easiest rule to break. Use a Serilog destructuring policy or a custom ITelemetryProcessor for Application Insights to scrub fields like password, authorization, and ssn before they leave the process.
Set up alerts that wake someone up
A log nobody reads is worse than no log because it creates false confidence. Configure alerts in Azure Monitor for spikes in 401s, 403s, 500s, and unusual geographic access patterns. Route them to a paging system, not just an inbox.
Securing the Deployment Pipeline
The API is only secure if the path from commit to production is secure too. This is where azure cloud migration services projects often uncover the biggest gaps.
Use managed identities, not connection strings
Azure managed identities eliminate the need to store database credentials, storage keys, or service principal secrets in app settings. The Azure.Identity package handles token acquisition transparently.
Scan container images and IaC
If you ship containers, run Trivy or Microsoft Defender for Containers on every build. For Bicep or Terraform, use checkov or tfsec to catch misconfigured network security groups and public storage accounts before they reach Azure.
Separate environments and least-privilege access
Dev, staging, and production should be separate Azure subscriptions or at minimum separate resource groups with distinct RBAC assignments. This is core to any azure landing zone implementation and to a proper azure architecture review.
Compliance Considerations for Regulated Industries
Generic security controls are necessary but not sufficient when HIPAA, PCI-DSS, SOX, or GDPR apply.
Map controls to the regulation
For a healthcare client, every control above maps to a specific HIPAA Security Rule safeguard. For PCI-DSS, requirement 6.5 explicitly calls out injection flaws, broken authentication, and insecure cryptographic storage. Document the mapping so auditors do not have to guess.
Implement Human-in-the-Loop governance for deployments
For banking and healthcare APIs, automated deployment to production without a human approval gate is a compliance risk. Configure Azure DevOps environments with required approvers, or use GitHub Actions environment protection rules. This is the governance model we apply across our power automate consulting and power platform governance engagements.
Keep an immutable audit trail
Azure Monitor logs can be exported to immutable storage with legal hold. For SOX and HIPAA, this is often the difference between a clean audit and a finding.
How This Checklist Fits into a Broader Modernization
Securing an API in isolation is useful. Securing it as part of a coordinated platform strategy is better. If you are also working through azure app modernization, an azure infrastructure assessment, or an azure security assessment, the controls above should be baked into your reference architecture, not retrofitted per service.
The attack surface of a modern .NET API is wider than most teams admit.
Most API breaches start with weak or missing authentication.
Knowing who the caller is does not tell you what they can do.
Trust nothing that comes in over the wire.
Unrestricted resource consumption is API Security Top 10 #4.
Conclusion
API security in .NET is not a single feature you turn on. It is a checklist you run on every endpoint, every release, and every dependency update. The controls above, strong authentication, resource-level authorization, strict input validation, rate limiting, encrypted transport, dependency scanning, structured logging, and governed deployment, are the minimum bar for any production .NET API in 2026. If your team is short on capacity to implement them, our api development services and azure consulting services can run a security assessment and ship the fixes within a single sprint. The longer you wait, the more expensive the eventual incident becomes. Start with authentication and authorization this week, and work down the list from there. Microsoft's official ASP.NET Core security documentation is a useful companion reference as you go.
Co-Founder and CTO, QServices IT Solutions Pvt Ltd
Rohit Dabra is the Co-Founder and Chief Technology Officer at QServices, a software development company focused on building practical digital solutions for businesses. At QServices, Rohit works closely with startups and growing businesses to design and develop web platforms, mobile applications, and scalable cloud systems. He is particularly interested in automation and artificial intelligence, building systems that automate routine tasks for teams and organizations.
The most common vulnerabilities in .NET APIs are broken object-level authorization (BOLA), weak JWT validation, over-posting through direct entity binding, missing rate limiting, and unscanned NuGet dependencies. ASP.NET Core provides the primitives to fix all five, but defaults are not secure enough on their own.
Use the AddJwtBearer middleware with TokenValidationParameters that explicitly validate the issuer, audience, lifetime, and signing key. Pin the issuer to your Microsoft Entra ID tenant or IdentityServer instance, and use the Microsoft.Identity.Web package rather than rolling custom token validation logic.
Yes. Internal does not mean trusted. A compromised internal service or a buggy client can still exhaust your thread pool or database connections. Use the built-in rate limiter introduced in .NET 8 with at least a concurrency limiter on expensive endpoints.
Never bind incoming requests directly to your EF Core entities. Always define DTOs that expose only the fields a client is permitted to set, then map to entities inside your service layer. This prevents attackers from setting fields like IsAdmin or TenantId through the JSON payload.
Use Azure Key Vault with managed identities. The Azure.Identity and Microsoft.Extensions.Configuration.AzureKeyVault packages let your application read secrets without ever storing connection strings or keys in app settings or environment variables.
On every build. Add dotnet list package –vulnerable as a required step in your CI pipeline and fail the build on high or critical findings. Pair it with Dependabot or Renovate for automated update PRs, and use a NuGet lock file so transitive updates do not slip in unnoticed.
Log authentication failures, authorization denials, rate limit hits, and any data-layer exceptions with structured properties for user ID, resource ID, and policy evaluated. Ship the logs to Azure Monitor or Log Analytics, scrub PII and tokens before logging, and configure alerts for spikes in 401s, 403s, and unusual geographic access patterns.
Business intelligence consulting services should give a mid-market company a governed way to make decisions. Attractive dashboards are only the visible part. The useful outcome is a system in which source data, metric definitions, access, releases, ownership, and support still work after the consultants leave.
In a Microsoft Solutions Partner vs Microsoft Partner comparison, the difference is validation. A company can participate in the Microsoft AI Cloud Partner Program without holding a customer-facing Solutions Partner designation. A designated Solutions Partner has met Microsoft’s current threshold in a specific solution pathway: at least 70 out of 100 partner capability points, with more than zero points in every required metric, based on performance, skilling, and customer success data recorded in Partner Center.
How do you build a legacy application modernization strategy for Azure? A legacy application modernization strategy assigns the right treatment to each workload, then sequences the work around business value, technical evidence, and operational risk. For Azure, that means choosing among retire, retain, rehost, replatform, refactor, rearchitect, rebuild, and replace instead of treating cloud migration as a blanket mandate. Direct Answer A legacy application modernization strategy for Azure should classify
Eager to discuss about your project?
Share your project idea with us. Together, we’ll transform your vision into an exceptional digital product!
Business intelligence consulting services should give a mid-market company a governed way to make decisions. Attractive dashboards are only the visible part. The useful outcome is a system in which source data, metric definitions, access, releases, ownership, and support still work after the consultants leave.
In a Microsoft Solutions Partner vs Microsoft Partner comparison, the difference is validation. A company can participate in the Microsoft AI Cloud Partner Program without holding a customer-facing Solutions Partner designation. A designated Solutions Partner has met Microsoft’s current threshold in a specific solution pathway: at least 70 out of 100 partner capability points, with more than zero points in every required metric, based on performance, skilling, and customer success data recorded in Partner Center.