Hitl regulated industries face a challenge that no compliance checklist can solve: the gap between what regulators want on paper and what actually happens when AI touches a patient record, a loan application, or a logistics decision. Human-in-the-loop governance is not a feature you bolt on after deployment. It is a delivery methodology that determines whether your ai augmented software development survives its first audit or collapses under scrutiny. This post breaks down what real HITL governance looks like, why most organizations get it wrong, and how a structured ai governance framework prevents the kind of expensive failures that show up in post-mortems, not sprints.
In This Article, You'll Learn
What HITL Governance Actually Means in Regulated Industries
Why 67% of Digital Transformations Fail in Regulated Environments
What a Real AI Governance Framework Includes
How Responsible AI Implementation Works in Practice
The Blueprint Sprint: Governance Before Code
Eager to discuss about your project?
Share your project idea with us. Together, we’ll transform your vision into an exceptional digital product!
What HITL Governance Actually Means in Regulated Industries
HITL regulated industries are not short on documentation. HIPAA binders, SOC 2 reports, ISO 27001 certificates. Most organizations have all of it. What they often lack is a process that ties human judgment to every consequential AI decision in a traceable, repeatable way.
Human-in-the-Loop (HITL) governance is a delivery methodology where human approval is required at every decision point in an AI-powered workflow. That definition sounds simple. The execution is not.
In a healthcare organization, this means a clinician reviews AI-generated triage recommendations before they influence care routing. In a bank, it means a compliance officer signs off on AI-flagged transactions before any customer action is taken. The AI handles pattern recognition at scale. The human handles judgment and accountability.
Beyond Compliance Checklists
Compliance checklists tell you what state to be in. They say nothing about how you got there, who made which decision, or what happens when the AI was wrong. A checklist might confirm your system has an audit log. It will not tell you whether that log captures the human approval chain at every step.
Regulators in healthcare, finance, and logistics are increasingly asking for evidence of process, not just outcomes. The HIPAA-compliant cloud architecture on Azure your team built last quarter may be technically correct. Whether it has a governed delivery process behind it is a separate question.
The Human Decision Layer That Regulators Actually Want
Regulators want to reconstruct any decision. If an AI system denied a loan or flagged a healthcare claim, they want to see who reviewed that output, when, and what they approved. That reconstruction requires more than logs. It requires a software delivery governance model that bakes checkpoints into the workflow, not just into the post-deployment audit.
This is the core of human in the loop ai governance: not AI with a review button, but a delivery process where human oversight is structural, not optional.
Why 67% of Digital Transformations Fail in Regulated Environments
According to McKinsey research on digital transformation, roughly 70% of digital transformations fail to meet their goals. In regulated industries, the consequences extend beyond missed deadlines to regulatory penalties, remediation cycles, and in healthcare, patient risk.
Key Insight According to McKinsey research on digital transformation, roughly 70% of digital transformations fail to meet their goals.
67% of enterprise digital transformations miss deadlines due to governance failures, not technology failures. The technology almost always works. What breaks is the decision chain: who approved what, when scope changed, and who signed off on a deployment that turned out to be non-compliant.
Key Insight 67% of enterprise digital transformations miss deadlines due to governance failures, not technology failures.
Governance Gaps vs. Technology Failures
When a software project fails in a bank or a hospital, the post-mortem usually blames the technology stack. Rarely does it name the real cause: there was no software project governance structure requiring human sign-off before each phase. Developers built what they thought was requested. Stakeholders approved what they thought was built. Nobody owned the gap between those two things.
This is exactly the problem that scope creep prevention through governance addresses. Scope creep and governance failures are the same failure expressed differently.
What Failed Transformations Have in Common
Projects that fail do so because there was no delivery governance framework forcing human checkpoints at the right moments. Not at the end, when damage is done. At each sprint gate, each integration decision, each deployment approval.
AI in software delivery amplifies this problem. When AI generates code or recommendations at speed, velocity increases. If governance doesn't keep pace, the risk compounds faster than any QA process can catch.
What a Real AI Governance Framework Includes
Most conversations about an ai governance framework focus on model ethics: bias detection, explainability, fairness. Those are real concerns. But for a CTO running delivery in a regulated industry, the more immediate concern is operational governance: who approves what before it ships?
A functional ai governance framework for software delivery includes five components:
Pre-build scoping: Human approval of requirements before development starts
Sprint gate reviews: Structured checkpoints at the end of each sprint, not just at deployment
AI output approval workflows: Explicit human review before AI-generated code or recommendations affect production
Immutable audit trails: Logs that cannot be altered after the fact, capturing every decision and its approver
Compliance mapping: Each checkpoint linked to the specific regulatory requirement it satisfies
Auditing is retrospective. You examine what happened. Governing is prospective. You define what must happen before the next step is allowed. HITL workflow automation makes governing practical at scale: the system enforces the checkpoint, the human satisfies it, and the audit trail records both.
Building Audit-Ready Software Delivery
Audit ready software delivery doesn't happen by accident. It requires governance checkpoints designed into the delivery process from the first sprint, not patched in before a regulatory review. Our approval workflow for AI-generated code reflects this principle: human approval is not a step that comes after development. It happens during development, at each meaningful decision point.
How Responsible AI Implementation Works in Practice
Responsible ai implementation is not a philosophy. It is a workflow. Most organizations treat it as the former and skip the latter entirely.
Every AI-generated output in a regulated industry needs a designated human reviewer, a defined review window, a documented decision, and a record meeting the evidentiary standard of the relevant regulator. In healthcare, that might mean 24-hour review cycles for AI diagnostic support. In banking, same-day sign-off for AI-flagged suspicious transactions.
Human Oversight in AI Systems: More Than a Review Button
Human oversight ai systems are often designed with a single review button at the end of a workflow. That is not governance. By the time a human sees the output, the model has already made hundreds of micro-decisions, and the human is being asked to ratify a conclusion they didn't participate in building.
Real human oversight means checkpoints at the decision nodes inside the workflow, not just at the output. The case for human approval before deployment makes exactly this point: human approval must precede deployment, not follow it.
HITL Workflow Automation That Regulators Can Trace
The goal of hitl workflow automation is to make human checkpoints frictionless enough that teams use them, and traceable enough that regulators can reconstruct them. For teams building ai augmented software development practices, this means choosing automation tools that generate governance-ready logs by default. Azure DevOps supports approval gates natively. The governance layer is a configuration decision, not a custom build.
The Blueprint Sprint: Governance Before Code
QServices developed the 5-day Blueprint Sprint specifically to address the governance gap that most software projects carry before a single line of code is written. Blueprint sprint methodology front-loads the decisions that most teams defer until they become expensive problems.
In five days, the Blueprint Sprint produces:
A defined scope with explicit change-control boundaries
A stakeholder approval matrix covering who signs off on what
A compliance checkpoint map tied to the delivery schedule
A risk register with mitigation owners
A delivery governance framework for the project's full lifecycle
How QServices Structures the 5-Day Blueprint Sprint
Day 1 focuses on requirements discovery and stakeholder mapping. Day 2 covers technical architecture with explicit security and compliance constraints. Day 3 produces the governance model: checkpoints, approvers, escalation paths. Day 4 stress-tests the plan against the regulatory environment. Day 5 produces a signed-off project charter that all parties commit to before development begins.
The full Blueprint Sprint breakdown explains why, in our client engagements, this upfront investment consistently saves far more than it costs in avoided rework downstream.
The compliance failures that surface during audits almost always trace back to a decision made early in the project without adequate human review. Someone assumed a system boundary. Someone interpreted a regulatory requirement without a compliance officer in the room. The Blueprint Sprint forces those conversations into a documented format before they become expensive corrections.
Software project governance that starts at scoping, not at deployment, is the difference between a project that passes its first audit and one that requires a six-month remediation cycle.
HITL vs. Fully Automated AI in Healthcare and Finance
The debate between HITL and fully automated AI is often framed as a speed question. Automation is faster. Humans are slower. Therefore: automate everything and use humans for exceptions only.
This framing fails in regulated industries. The question is not speed. It is accountability.
Where Automation Should Stop
Automation should stop at any decision point where the consequences of an error are regulatory, financial, or clinical. That is not a technological line. It is a governance line. A model can flag a fraudulent transaction with 99.7% accuracy. That 0.3% error rate, applied to millions of daily transactions, produces thousands of wrongful flags per day. A human checkpoint at the flag-to-action step is not a bottleneck. It is a necessary control.
Key Insight A model can flag a fraudulent transaction with 99.7% accuracy.
According to NIST's AI Risk Management Framework, human oversight is a foundational requirement for AI systems in high-stakes domains. The framework does not treat this as a best practice. It treats it as a baseline expectation.
Industry-Specific Checkpoints That Protect You
In healthcare, the checkpoints are clinical: AI recommendations require physician review before influencing care decisions. In financial services, they are compliance-driven: AI-flagged items require analyst sign-off before customer communication. In logistics, they are operational: AI routing changes require dispatcher confirmation before fleet-level implementation.
The sprint governance model for agile delivery shows how these checkpoints fit inside a delivery cadence without destroying velocity. Governance slows bad decisions and speeds up good ones.
How to Measure Whether Your Software Delivery Governance Is Working
Governance is treated as a cost center when nobody measures its outputs. Organizations cannot demonstrate governance value to leadership, investment erodes, and the compliance failures that follow get blamed on technology.
Measurable outputs from a delivery governance framework include:
On-time delivery rate: QServices maintains a 98.5% on-time delivery rate across 500+ projects using HITL governance, measured from Blueprint Sprint charter to final deployment
First-pass audit rate: What percentage of deliverables pass internal or external audit without rework?
Scope change frequency: How often does scope change after the initial charter? Fewer changes indicate governance is working at the scoping stage
Defect escape rate: How many defects reach production? Human checkpoints at sprint gates reduce this measurably
Time to regulatory response: When an auditor asks for documentation, how quickly can you produce it? Audit ready software delivery should produce documentation in hours, not weeks
Metrics That Matter to Auditors
Auditors in regulated industries care about three things: completeness of documentation, traceability of decisions, and evidence of human oversight at consequential steps. If your delivery governance framework cannot produce a complete decision trail for any project within four hours, it is not audit-ready.
Why Weekly Demos Belong in Your Governance Stack
One of the most underrated governance tools in software delivery is the weekly client demo. Not as a status update, but as a structured accountability checkpoint. Weekly client demos as a governance mechanism explains how a 30-minute weekly session, properly structured, generates documented stakeholder alignment that auditors look for and prevents the delivery failures that derail regulated projects.
Key Takeaways
HITL regulated industries are not short on documentation.
According to McKinsey research on digital transformation, roughly 70% of digital transformations fail to meet their goals.
Most conversations about an ai governance framework focus on model ethics: bias detection, explainability, fairness.
Responsible ai implementation is not a philosophy.
QServices developed the 5-day Blueprint Sprint specifically to address the governance gap that most software projects carry before a single line of code is written.
Conclusion
Hitl regulated industries don't need more compliance documentation. They need delivery processes where human judgment is embedded at every decision point, traceable from start to finish, and measurable in ways that matter to both leadership and regulators. That is what human in the loop ai governance delivers when it is built into a project from day one rather than retrofitted after the fact.
The Blueprint Sprint, structured sprint gates, AI output approval workflows, and immutable audit trails are not overhead. They are the delivery governance framework that lets regulated organizations adopt AI confidently. Responsible ai implementation at the enterprise level starts with a methodology, not a policy document.
Co-Founder and CTO, QServices IT Solutions Pvt Ltd
Rohit Dabra is the Co-Founder and Chief Technology Officer at QServices, a software development company focused on building practical digital solutions for businesses. At QServices, Rohit works closely with startups and growing businesses to design and develop web platforms, mobile applications, and scalable cloud systems. He is particularly interested in automation and artificial intelligence, building systems that automate routine tasks for teams and organizations.
Human-in-the-Loop (HITL) governance is a delivery methodology where human approval is required at every consequential decision point in an AI-powered workflow. It is not a single review button at the end of a process. It is a structured framework of checkpoints, approvers, and immutable audit trails embedded throughout the software delivery lifecycle. In regulated industries, HITL governance ensures that AI-generated outputs, code, and recommendations all require documented human sign-off before they affect production systems or end users.
67% of enterprise digital transformations miss deadlines due to governance failures, not technology failures. The technology typically works. What breaks is the decision chain: who approved changes, when scope shifted, and who signed off on deployments that turned out to be non-compliant. Without a delivery governance framework that enforces human checkpoints at sprint gates and deployment approvals, projects drift until they fail. Governance gaps, not technology gaps, are the leading cause of failed transformations in regulated industries.
A blueprint sprint is a structured 5-day engagement that front-loads governance decisions before a single line of code is written. Developed by QServices, it produces a defined scope with change-control boundaries, a stakeholder approval matrix, a compliance checkpoint map tied to the delivery schedule, a risk register with mitigation owners, and a signed project charter. Blueprint sprint methodology reduces downstream compliance failures by forcing regulatory and governance conversations into a documented format at the project start, not after expensive rework has begun.
Audit-ready AI development requires governance checkpoints designed into the delivery process from the first sprint. This means pre-build scoping with documented human approval, sprint gate reviews with sign-off requirements, AI output approval workflows before production deployment, immutable audit trails capturing every decision and its approver, and compliance mapping linking each checkpoint to the specific regulatory requirement it satisfies. If your delivery governance framework can produce a complete decision trail for any project within four hours, it meets the standard for audit ready software delivery.
In fully automated AI, the system makes decisions end-to-end without requiring human approval at consequential steps. In HITL systems, human review is embedded at defined decision nodes, particularly where errors carry regulatory, financial, or clinical consequences. For hitl regulated industries like healthcare, banking, and logistics, the hybrid approach is necessary: AI handles pattern recognition and speed, while humans handle accountability and judgment at checkpoints that regulators can trace and reconstruct.
Adding governance to agile delivery means embedding human checkpoints at sprint gates rather than only at final deployment. Practically, this includes a documented Definition of Ready before each sprint, stakeholder sign-off at each sprint demo, explicit approval workflows for AI-generated code before merging, and an immutable audit trail capturing every approval decision. Sprint governance does not slow agile delivery. It slows bad decisions while accelerating team alignment on what was actually approved and why.
A functional ai governance framework for software delivery includes five components: pre-build scoping with human approval of requirements, sprint gate reviews at each delivery checkpoint, AI output approval workflows before production impact, immutable audit trails capturing every decision and its approver, and compliance mapping linking each checkpoint to the specific regulatory standard it satisfies. An AI governance framework is distinct from an AI ethics policy. Ethics policy defines principles. A governance framework defines the operational process that enforces those principles during delivery.
Azure migration cost breaks down by workload strategy, not a single number. See real per-workload ranges, what FastTrack and Azure Migrate and Modernize actually cover, and how a fixed-price Blueprint Sprint replaces a vague estimate with a firm quote.
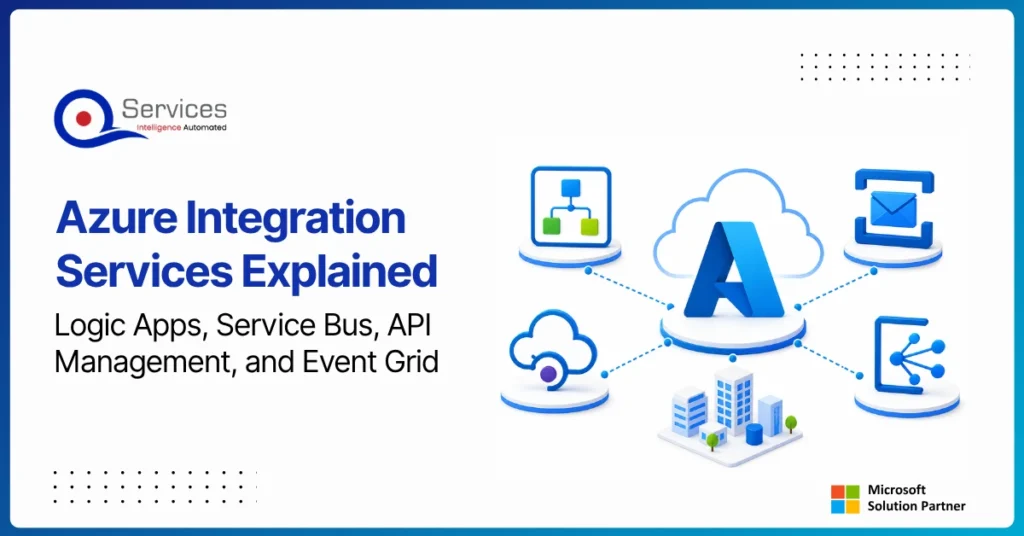
Azure Integration Services is Microsoft’s suite of cloud-native tools for connecting applications, data, and processes across your enterprise. When your organization runs a mix of on-premise systems, SaaS platforms, and custom APIs, getting them to communicate reliably is one of the hardest operational problems you will face. Azure integration services address that directly with four purpose-built components: Logic Apps for workflow automation, Service Bus for reliable messaging, API Management for governing APIs at scale, and Event Grid for event-driven architecture.
Key Insight Azure Integration Services is Microsoft’s suite of cloud-native tools for connecting applications, data, and processes across your enterprise.
This guide breaks down each component, explains how they work together, and covers when azure cloud migration services can bring your entire integration layer into the cloud. Teams evaluating azure consulting services for the first time will find the service breakdowns most useful. Teams already planning a lift and shift to azure should jump straight to the migration section.
Power BI Embedded is Microsoft’s developer-focused API for embedding interactive analytics directly inside third-party apps, customer portals, and SaaS products. If you are building software and want customers to see live dashboards without logging into the Power BI service, this is where that journey starts. The question is not whether you can embed Power BI reports, you almost certainly can. The real question is whether it makes financial and architectural sense for your specific situation. This guide covers the when, the how, and the cost math that most tutorials skip.
Power apps portals sit at an interesting crossroads for IT leaders: they’re fast, deeply integrated with the Microsoft stack, and manageable without a dedicated development team. But they’re also constrained in ways that matter when your business needs a portal that handles complex UI logic, third-party integrations outside the Microsoft ecosystem, or pixel-perfect UX design.
This guide gives you a straight comparison so you can make the right call without spending three months in discovery. We’ll cover what each option actually delivers, where each breaks down, and the governance questions that need answers before you commit either way.
If you’re evaluating your Microsoft stack more broadly, our breakdown of Power Platform vs Custom .NET Development provides useful parallel context.
Azure migration cost breaks down by workload strategy, not a single number. See real per-workload ranges, what FastTrack and Azure Migrate and Modernize actually cover, and how a fixed-price Blueprint Sprint replaces a vague estimate with a firm quote.
Azure Integration Services is Microsoft’s suite of cloud-native tools for connecting applications, data, and processes across your enterprise. When your organization runs a mix of on-premise systems, SaaS platforms, and custom APIs, getting them to communicate reliably is one of the hardest operational problems you will face. Azure integration services address that directly with four purpose-built components: Logic Apps for workflow automation, Service Bus for reliable messaging, API Management for governing APIs at scale, and Event Grid for event-driven architecture.
Key Insight Azure Integration Services is Microsoft’s suite of cloud-native tools for connecting applications, data, and processes across your enterprise.
This guide breaks down each component, explains how they work together, and covers when azure cloud migration services can bring your entire integration layer into the cloud. Teams evaluating azure consulting services for the first time will find the service breakdowns most useful. Teams already planning a lift and shift to azure should jump straight to the migration section.
Power BI Embedded is Microsoft’s developer-focused API for embedding interactive analytics directly inside third-party apps, customer portals, and SaaS products. If you are building software and want customers to see live dashboards without logging into the Power BI service, this is where that journey starts. The question is not whether you can embed Power BI reports, you almost certainly can. The real question is whether it makes financial and architectural sense for your specific situation. This guide covers the when, the how, and the cost math that most tutorials skip.
Power apps portals sit at an interesting crossroads for IT leaders: they’re fast, deeply integrated with the Microsoft stack, and manageable without a dedicated development team. But they’re also constrained in ways that matter when your business needs a portal that handles complex UI logic, third-party integrations outside the Microsoft ecosystem, or pixel-perfect UX design.
This guide gives you a straight comparison so you can make the right call without spending three months in discovery. We’ll cover what each option actually delivers, where each breaks down, and the governance questions that need answers before you commit either way.
If you’re evaluating your Microsoft stack more broadly, our breakdown of Power Platform vs Custom .NET Development provides useful parallel context.